Get DeafLetter
A weekly selection of signals, vulnerabilities and guides. Critical alerts remain optional.
You can unsubscribe at any time. Privacy policy.
Attackers are actively exploiting CVE-2026-58115, a maximum-severity vulnerability in the Node-RED component of Siemens SIMATIC IoT2050 industrial gateways. The first documented observation dates to October 30, 2026, when VulnCheck researchers detected exploits against their honeypots. The severity of this case goes beyond the CVSS 10.0 score: the backdoor mechanism persists because malicious Node-RED flows survive device reboots, making configuration verification necessary in addition to firmware updates.
- CVE-2026-58115 is classified CWE-306 (Missing Authentication for Critical Function) with CVSS 10.0 in both version 3.1 and 4.0, per the official cve.org record
- The active exploit observed on October 30, 2026 uses a single POST /flows request with triple-layer encoding to deploy bot binaries and install persistent HTTP backdoors
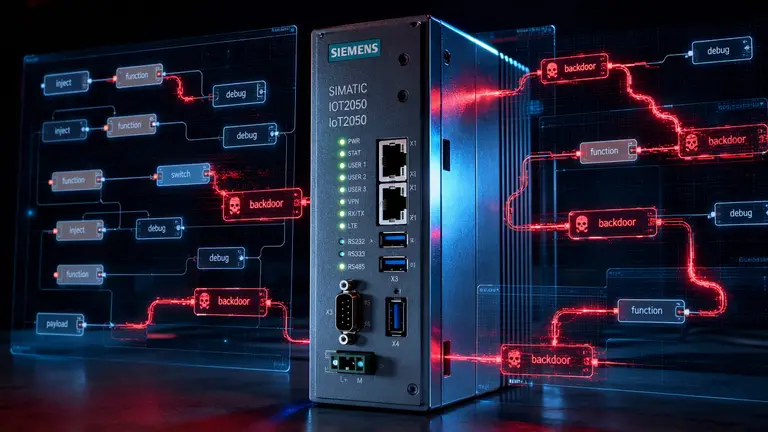
- The backdoor configures as an internal HTTP endpoint within Node-RED, linked to an exec node with elevated privileges, and maintains access after reboots because it is saved in the flow configuration
- Siemens released the fix in August 2026 with version V4.3.4-1; the patch does not remove pre-existing compromised flows
- Observations come exclusively from VulnCheck honeypots: no compromise of production devices is confirmed
The Attack Mechanism: One Request, Three Encoding Layers
The exploit requires no authentication. The Node-RED HTTP interface, when no credentials are configured, accepts remote requests that modify data-processing flows. According to Patrick Garrity, a VulnCheck researcher, "the attacker's request was a complete exploit: it deployed a Node-RED flow, triggered it automatically, and downloaded a binary from an attacker-controlled server, all behind three levels of encoding."
The binary, named bot-linux-amd64, is downloaded via wget or curl from 85.215.73[.]250 into the /dev/shm/.b directory. This placement in volatile memory means the bot would not survive a reboot. The operators anticipated a second stage, however: the wget.sh script retrieved from the same server and the .sys_update file from 45.194.90[.]57:38472, saved as /tmp/.kworker. VulnCheck was unable to retrieve these payloads for analysis; their functionality remains unknown.
The persistent component is an HTTP endpoint configured inside the Node-RED flow, typically on paths such as /cmd or random names. The flow includes a function node linked to an exec node with the addpay parameter enabled, which executes received HTTP commands with maximum privileges on the underlying operating system. Because Node-RED flows are saved in the device's persistent configuration, the backdoor survives reboots: persistence is inherent to the Node-RED configuration, not to a memory-resident malware.
"This backdoor survives even if a memory-resident implant is lost on reboot" — Patrick Garrity, VulnCheck
The Attacker Profile: Opportunism, Not Targeted APT
The IP address 4.201.105[.]116, geolocated in Brazil within Microsoft cloud address space AS8075, does not belong to a targeted operation against specific sectors. Between October 30 and November 1, 2026, the same address sent 16 exploit attempts against the Siemens vulnerability and 125 total requests distributed across 8 different CVEs, according to VulnCheck data reported by SQ Magazine.
The activity includes scans against vulnerabilities in Apache Solr, Gitea, MLflow, Traefik, and Joomla, some seven years old. This profile is consistent with an opportunistic mass-scanning operation, not a campaign attributable to an advanced persistent threat actor. The identity of the operators and their motive do not emerge from available data.
Why the Patch Is Not Enough to Remediate
Siemens published advisory SSA-834709 and made firmware V4.3.4-1 available in August 2026. The fix covers four product variants — IoT2050 Advanced, Basic, M.2, and SM — all with Industrial OS and Node-RED installed. Installing the update, however, does not remove any compromised Node-RED flows present in the configuration.
IoT2050 gateways typically operate as bridges between plant networks (OT) and IT or cloud infrastructure. Compromise of these devices allows arbitrary code execution with maximum privileges on the underlying operating system, with potential impact on connected industrial control segments.
The roughly three-month gap between patch publication and the start of active exploitation is documented in VulnCheck data. No data emerges on the total number of IoT2050 systems exposed on the Internet or on any compromises in non-honeypot environments.
Remediation Steps
- Verify for anomalous flows in the Node-RED configuration of every IoT2050 device, looking for undocumented HTTP endpoints or exec nodes linked to web inputs
- Update to firmware V4.3.4-1 or later for all affected variants, following the official Siemens advisory SSA-834709
- Uninstall Node-RED if not required for the gateway's operational functions, eliminating the attack surface
- Enforce authentication on the Node-RED HTTP interface where operations require it, using supported modes (credentials, OAuth, OpenID, or basic auth)
Source Limitations and Context
Observations on CVE-2026-58115 come exclusively from VulnCheck honeypots: no compromise of production devices is confirmed. VulnCheck was unable to retrieve the wget.sh and .sys_update payloads for analysis, nor has it analyzed the bot-linux-amd64 binary: the bot's actual functionality remains unknown. The CVE does not appear in the CISA KEV catalog as of the available sources.
The backdoor's persistence is an effect of Node-RED's architecture, where flows are configuration files saved to disk: a reboot reloads them automatically. The patch fixes the missing-authentication vulnerability but does not scan or remove pre-existing configurations. This distinction is material for incident response: a firmware update without flow verification leaves an already-installed backdoor active.
The Core Issue
CVE-2026-58115 is classified CWE-306: Missing Authentication for Critical Function. The official cve.org record assigns the maximum score of 10.0 in both CVSS 3.1 and 4.0. Authentication for the Node-RED HTTP interface is not mandatory by default in the affected configuration, allowing unauthenticated remote requests that modify processing flows.
This characteristic, combined with Node-RED's ability to execute system commands via the exec node, turns a single HTTP request into a remote execution vector with elevated privileges. Once saved, malicious flows become indistinguishable from legitimate configurations unless manually inspected.
Patrick Garrity of VulnCheck described the vulnerability as "trivial to weaponize." The exploit's simplicity — a single unauthenticated POST request — explains the inclusion of CVE-2026-58115 in a mass-scanning campaign against diverse, multi-sector targets.
Sources
- thehackernews.com
- sqmagazine.co.uk
- dev.to
- securitypointbreak.com
- cve.org
- cert-portal.siemens.com
- cisa.gov
- news.lavx.hu
- techzine.eu
- threat-intelligence.redeyesecurity.com
Get DeafLetter
A weekly selection of signals, vulnerabilities and guides. Critical alerts remain optional.
You can unsubscribe at any time. Privacy policy.