Cybersecurity
Cybersecurity collects analysis on vulnerabilities, exploits, patch management, ransomware, supply chain, AI security and threat intelligence. These articles help IT professionals, developers and security analysts follow operational threats, vendor updates and technical trends.
OriginLab Origin Viewer: RCE Patch for OGW Files, ZDI Disclosure
Trend Micro's Zero Day Initiative (ZDI) has disclosed vulnerability ZDI-26-553 in the OriginLab Origin Viewer OGW file parser. The ven…
CVE-2026-54984: RCE in Windows ICC Parser, but the Vector Is Local
Microsoft patched CVE-2026-54984, an RCE vulnerability in the Windows color management component. The CVSS indicates a local attack ve…
Flowise Pre-Auth RCE, CVSS 9.8: Update Immediately to 3.1.3
ZDI-26-546 discloses a critical flaw in the low-code Flowise platform. The Airtable_Agent component executes Python code without valid…
Microsoft Rates Exploitation 'More Likely' for CVE-2026-62893 in Windows
Microsoft patched a use-after-free in the WDSServer service of Windows Deployment Services. The exploitability assessment is 'More Lik…
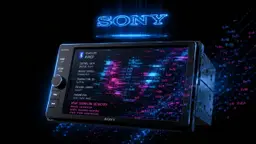
Sony XAV-9500ES: AVRCP Heap Overflow Enables RCE via Bluetooth
The ZDI-26-475 vulnerability (CVE-2026-18282, CVSS 8.0) in the Sony XAV-9500ES Bluetooth AVRCP parser allows remote code execution aft…
Red Hat ACM: Subscription Controller Becomes Bridge for Total Privilege Escalation
A vulnerability in Red Hat Advanced Cluster Management allows users with edit permissions on a single namespace to gain full cluster-a…
TrendAI Vision One: Log Information Disclosure Fixed After 10 Months
The TrendAI Vision One security platform has closed CVE-2025-71386, an information disclosure vulnerability in Service Gateway logs. H…
Lazarus Strikes with CVE-2026-68820: Microsoft Zero-Day in Defense Sector
Check Point discovers the 2026 wave of Operation Dream Job. Lazarus exploits CVE-2026-68820 in AFD.sys to deploy FudModule via fake jo…
Kenwood DNR1007XR: Firmware Update Flaw Enables Root RCE via Symlink Following
A vulnerability in the Kenwood DNR1007XR firmware update process allows a physically present attacker to achieve arbitrary code execut…
Head Mare APT Turns TrueConf Servers into Supply-Chain Attack Vehicles
The Head Mare APT group exploited two zero-day vulnerabilities in TrueConf Server to distribute the PhantomCore and PhantomGraph backd…
Intellexa: Leaked Documents Expose 14 Zero-Days and Vendor Remote Access to Government Clients
Internal documents stolen from mercenary spyware vendor Intellexa reveal a systematic inventory of at least 14 zero-days for Android,…
Local Malware Bypasses Google Passkeys: The Flaw Is in Chrome, Not FIDO2
Palo Alto Networks Unit 42 research demonstrates that local malware can bypass FIDO2 passkeys in Chrome on Windows using three techniq…