Get DeafLetter
A weekly selection of signals, vulnerabilities and guides. Critical alerts remain optional.
You can unsubscribe at any time. Privacy policy.
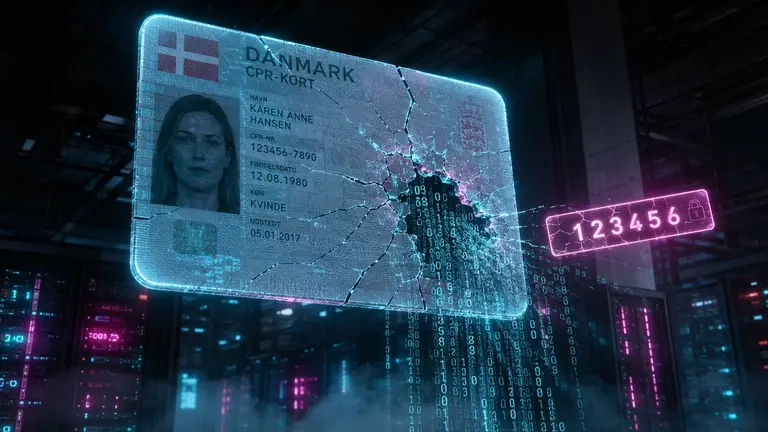
On the evening of October 2, 2026, Danish authorities detected an anomaly in the CPR system, the national identity register: unauthorized access lasting more than three weeks had extracted data associated with approximately 8.8 million CPR numbers, covering nearly the country's entire registered population. The breach was not a zero-day vulnerability in the government system, but the administrative account of Pays ApS, a micro IT company based in Odense with two employees as of July 2026, which managed legitimate access to the database with weak credentials.
- Pays ApS, a two-employee IT firm with legitimate access to the Danish CPR system, was the entry point for the extraction of data on approximately 8.8 million people
- Unauthorized access began on September 10, 2026; sources report conflicting durations: 21 days and 17 hours according to Cybernews, or "about 10 days" according to CSO Online
- The password '123456' is cited as an access element, included in at least three accounts, one with administrative privileges, according to an anonymous hacker's statements to Politiken reported by editorial sources
- Exposed data includes names, addresses, and CPR numbers; records with protected names and addresses were not involved, according to the CPR Administration statement
How Two Employees and a Trivial Password Opened the Entire National Register
Pays ApS operates in the Danish IT sector with authorized access to the Centrale Personregister, the database that assigns and manages CPR numbers — the Danish equivalent of a tax ID, used for every interaction with the state, from healthcare to taxation. Managing director Sophie Laursen confirmed to TV 2, reported by the Copenhagen Post and cited by Cybernews: "We can confirm that we are the company that has been subjected to an attack where our legal access to search for information in the CPR system has been abused."
According to the anonymous hacker's statements reported by Politiken and disseminated by specialized editorial sources, the attacker used a stolen password from a former employee to access three Pays ApS accounts, at least one with administrative privileges. The password '123456' is cited in this context, though sources present it as "reportedly" or "allegedly" based solely on the hacker's declaration, without independent forensic confirmation. The attacker reportedly created two automated programs to extract data from the system.
The technical mechanism is the abuse of legitimate access: not a breach of the CPR perimeter, but the use of valid credentials from an authorized third party for massive and anomalous queries. This architecture, where external entities of any size operate with direct access to centralized government systems, turns every single account into a potential single point of failure.
Over 14 Million Queries and No Automatic Shutdown
CSO Online reports an additional data point not present in other sources: over 14 million searches conducted through the compromised account, returning approximately 8.8 million records. This query volume, distributed over a timeframe sources place between 10 and 21 days, did not trigger automatic interruption mechanisms in the CPR system.
"A compromised account at a single supplier can bypass an organization's core security controls and turn a legitimate connection into a massive data exposure" — Dray Agha, senior manager of security operations at Huntress
The discrepancy on duration is significant and unexplained in the dossier: Cybernews cites "21 days and 17 hours, beginning on September 10th," while CSO Online indicates "about 10 days" for the access period. The dossier does not clarify whether sources refer to different activity periods, distinct incident phases, or reporting errors. The start date — September 10, 2026 — is consistent across sources; detection is fixed on the evening of October 2, 2026, per the CPR Administration statement.
The precise number of exposed records, according to Politiken cited by Cybersecurity News, is 8,749,975: 5.5 million living individuals and 3.3 million deceased. The figure is rounded to "approximately 8.8 million" in headlines and the official statement. Out of 11 million total individuals in the CPR system, the exposure covered nearly the entire registered universe, including residents, deceased, and emigrants.
Government Response and Dossier Gaps
The CPR Administration issued a press release on the evening of October 2, 2026, confirming the exposure of names, addresses, and CPR numbers and specifying that records with protected names and addresses — typically individuals under witness protection or victims of violence — were not involved. Authorities revoked Pays ApS access, reported the incident to the Danish Data Protection Authority, and launched an investigation with the National Special Crime Unit.
Minister Christina Egelund, responsible for Research, Education, and Digitalization, called the incident "deeply serious" and announced a "comprehensive mapping" of the case. MitID, the Danish two-factor authentication system, reduces the risk of direct impersonation via CPR numbers alone, though the combination of names, addresses, and identifiers exposes citizens to significant risks of targeted phishing and social engineering.
The dossier has documentary gaps on several points. It does not emerge whether the password '123456' was forensically verified or remains solely the anonymous hacker's declaration. It is unknown whether the attacker acts alone or as part of a structured group, or whether the data was actually sold or shared beyond delivery to Politiken. Authorities have not disclosed the status of the National Special Crime Unit investigation or any sanctions against Pays ApS.
What to Do Now
Exposed Danish citizens must assume the combination of name, address, and CPR number is in circulation and act accordingly. Three specific actions are immediately relevant for this case.
Monitor incoming communications with heightened suspicion. The exposure of name, address, and CPR makes highly personalized phishing emails and messages plausible, citing correct data to build trust. Always verify the origin of requests citing the CPR, even if apparently from public entities.
Verify that MitID is active and correctly configured. The two-factor system is the primary barrier against direct impersonation of government services using exposed CPR numbers alone. Do not disable login notifications and refuse unsolicited authentication requests.
Request information from the CPR Administration on the "comprehensive mapping" announced by Minister Egelund. The dossier does not document individual verification portals, but pressure on official channels for timelines and communication methods to affected individuals is the only available tool to obtain specific confirmation of one's own involvement.
Questions and Answers
Why is the Danish CPR number so sensitive?
The CPR is the unique identifier assigned to every Danish resident, deceased person, or emigrant. It is required for every public service and many private ones, making its combination with name and address an effective tool for targeted phishing and social engineering, even though MitID two-factor authentication prevents direct impersonation of government services.
What is the "name and address protection" mentioned in the sources?
The dossier cites the CPR Administration statement that records with "protected name and address" were not exposed. This category, common in Nordic registers, protects individuals in specific risk situations (witness protection, stalking, domestic violence). The dossier does not specify how many records fall into this category.
Can citizens verify if their data was exposed?
The dossier does not document individual notification tools or verification portals made available by authorities. The CPR Administration and the ministry have announced a "comprehensive mapping," but no details emerge on timelines or methods of communication to affected individuals.
Information is based on cited sources and current as of publication.
Information is based on the cited source and current as of publication.
Sources
- https://cybernews.com/security/denmark-cpr-data-breach-weak-password/
- https://cybersecuritynews.com/admin-password-danish-data-breach/
- https://cybernews.com/security/denmark-cpr-data-breach-exposes-millions/
- https://www.csoonline.com/article/4231797/denmarks-national-id-system-breach-exposes-personal-data-of-8-8m.html
Get DeafLetter
A weekly selection of signals, vulnerabilities and guides. Critical alerts remain optional.
You can unsubscribe at any time. Privacy policy.