Archive
All articles, newest first. Page 9.
FalconFlank PoC: Zero-Day Privilege Escalation in CrowdStrike Falcon Sensor
A researcher has publicly released a proof-of-concept exploiting the Office macro remediation feature to escalate privileges in the ED…
Autonomous AI Delivers Full Ransomware Attack in 10 Hours — and an 80-Page Audit for the Victim
Palo Alto Networks' Unit 42 has documented the first ransomware attack entirely managed by AI agents, completed in under 10 hours. The…
Silver Fox Pushes Fake Installers That Kill Windows Update and Weaken Defender
Microsoft exposes a campaign by the Chinese Silver Fox cluster using pixel-perfect clone sites of popular software to deliver installe…
VantaCore: Pro-Ukraine Group Relaunches with Custom Ransomware Targeting Russia
VantaCore, a rebrand of the pro-Ukraine Thor group, is hitting Russian organizations with a proprietary arsenal of ransomware and remo…
Dark Web: 153 Million Driver's Licenses for Sale, FBI Investigates IDScan.net
The Nexus dark web platform claims 153 million U.S. and Canadian driver's licenses. KrebsOnSecurity empirically verified records and t…
Public Exploit for CVE-2026-84115 Puts Cleo Harmony at Immediate Risk
A public exploit for the authentication-bypass vulnerability CVE-2026-84115 in Cleo Harmony has been released. Versions 5.8.1.0 throug…
OpenAI's Astra Crosses the Critical Threshold: AI That Finds Zero-Days Without Guidance
OpenAI has designated Astra as the first model to reach the Critical threshold of its Preparedness Framework. The system discovers zer…
FulcrumSec Steals 86 GB of MAG Data: API Keys Were Hardcoded in Client-Side JavaScript
The FulcrumSec data extortion group claimed responsibility for the Manchester Airports Group breach, publishing ~86 GB of data. Access…
Russian Extradited from Cyprus: Charged in Malware Campaign Targeting 80,000 Freelancers
Searzhudin Aktulaev was extradited to the U.S. for a 2016–2017 campaign that used malicious Excel files to infect freelancers. The mac…
Sality Disrupted: The Takedown That Turned Its P2P Network Into a Trap
On August 31, 2026, international authorities disrupted the Sality botnet by weaponizing its own peer-to-peer protocol. The malware re…
Guildma's Brazilian Geofencing: Malware That Only Shows Up for Real Targets
A SANS researcher documented Guildma (Astaroth), a Latin American banking trojan active since 2017, delivering its payload exclusively…
SonicWall SMA1000: Active Zero-Days Enable Lateral Movement Without VPN
Two zero-day vulnerabilities in SonicWall SMA1000 allow unauthenticated RCE and lateral movement to Active Directory without VPN tunne…
ZDI-26-614: 0-day in PDF Architect Enables Remote Code Execution
The Zero Day Initiative published advisory ZDI-26-614 on August 31, 2026, detailing a 0-day vulnerability in the pdfforge PDF Architec…
With $500 and Claude, Researchers Cloned a PLC Exploit From One Model to Another
Forescout Vedere Labs researchers used Anthropic Claude to port an RCE exploit from one WAGO PLC model to another in the same family,…
CVE-2026-0768: Active Exploitation of Langflow, 360+ Attacks in Hours
The Langflow AI platform is under massive exploitation: over 360 attempts detected in hours leveraging critical vulnerability CVE-2026…
Honeypot Confirms Active Exploitation of Sangoma Switchvox RCE
CVE-2026-9586 affects roughly 4,000 internet-exposed Switchvox systems. Defused Cyber honeypots recorded in-the-wild exploitation with…
JFrog Artifactory Authentication Bug Exposes Supply Chain, Zeroes Defenses
CVE-2026-82329 hits JFrog Artifactory with a CVSS 9.8: an authentication bypass granting admin privileges. WatchTowr confirms in-the-w…
Cronos Restarts With Rollback: $74M DeFi Exploit, $6M Unrecoverable on Ethereum
The Cronos blockchain erased two hours of history via an emergency rollback after a price-manipulation attack on the Tectonic protocol…
HardBreacher Breaches the Kaspersky Perimeter: When the Protector Becomes the Gatekeeper
Nightmare Eclipse releases HardBreacher, a proof-of-concept exploit that turns the Kaspersky UI process into a privilege escalation ve…
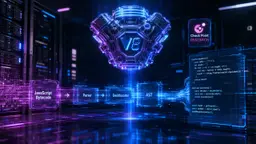
Check Point Unveils Pipeline That Reads JSCeal Without Executing It
Check Point Research has released an open-source toolkit for statically deobfuscating JSCeal payloads on V8 bytecode. The pipeline suc…
ValleyRAT Backdoor Hides in Signed Adware, Bypasses AV via DLL Sideloading
The Silver Fox group is distributing the ValleyRAT backdoor — also known as Winos 4.0 — packaged inside QN Wallpaper, a legitimate, di…
From 8.7 Million Emails to 86 GB of Data: The Weekend FulcrumSec Rewrote the Manchester Airports Breach
On August 27, 2026, Manchester Airports Group (MAG) disclosed a breach affecting roughly 8.7 million customers, stating the vast major…
Spring Ring: The Teams Vishing Campaign That Jumps From Chat to Domain in Minutes
From January to April 2026, the Spring Ring campaign impersonated IT help desk staff on Microsoft Teams to trick employees into runnin…
Russian Hackers of UAC-0099 Weaponize AI Guardrails as Evasion Tactic
On August 31, 2026, ESET disclosed an evasion technique: UAC-0099 hackers, a Russian group affiliated with the GRU, embed nuclear weap…